-

WordPress 7.1.3 Security Release: What Changed and How to Confirm Your Site Has It
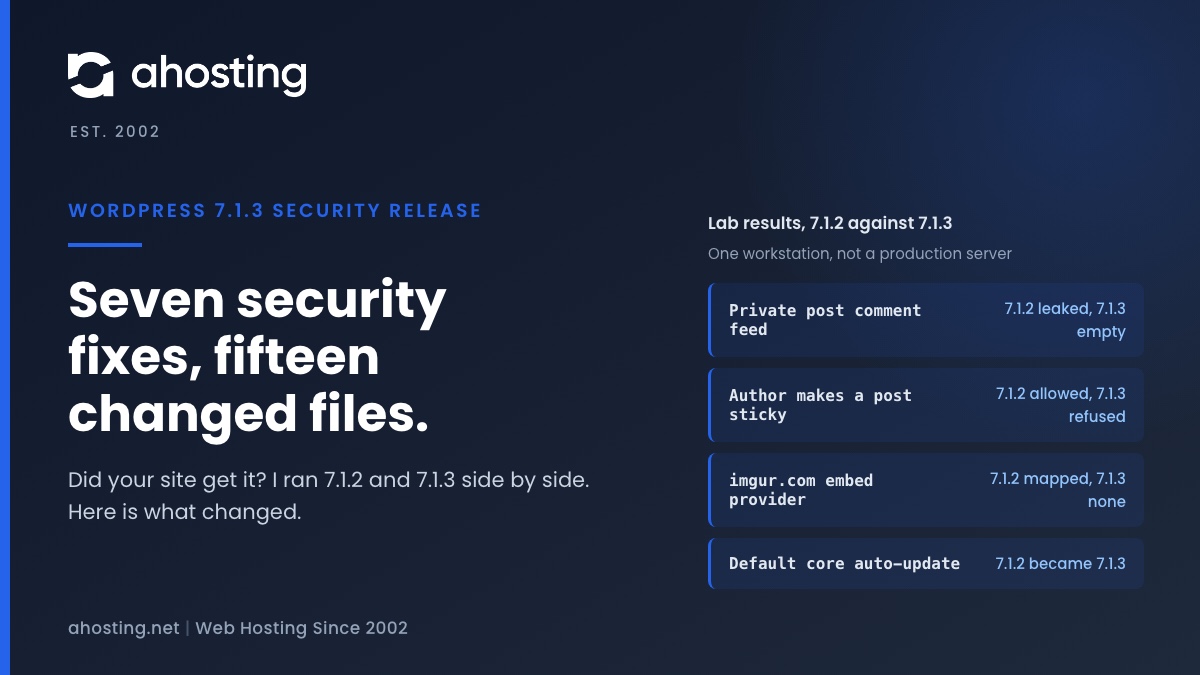
TL;DRThe WordPress 7.1.3 security release shipped on 6 October 2026 with seven security fixes and four bug fixes. Read your version under Tools, Site Health, Info, WordPress; 7.1.2 or any earlier 7.1 release needs the update. Minor releases install themselves by default, but a handful of switches stop that. In my lab, 7.1.2 handed an anonymous visitor the comments on a private post and a draft post and let an Author account make posts sticky; 7.1.3 refused both. WordPress published no CVE IDs, and none of the coverage I opened reports exploitation.
Categories
- CMS
- Concrete5
- Drupal
- FFmpeg / Video Hosting
- Hosting Guides
- How To
- Joomla
- Security
- SEO
- Uncategorized
- Video Content
- Web Hosting News
- WooCommerce
- WordPress
Lets Connect!
-
PHP Security Update: 8.5.12, 8.4.27, 8.3.36 and 8.2.35 for WordPress
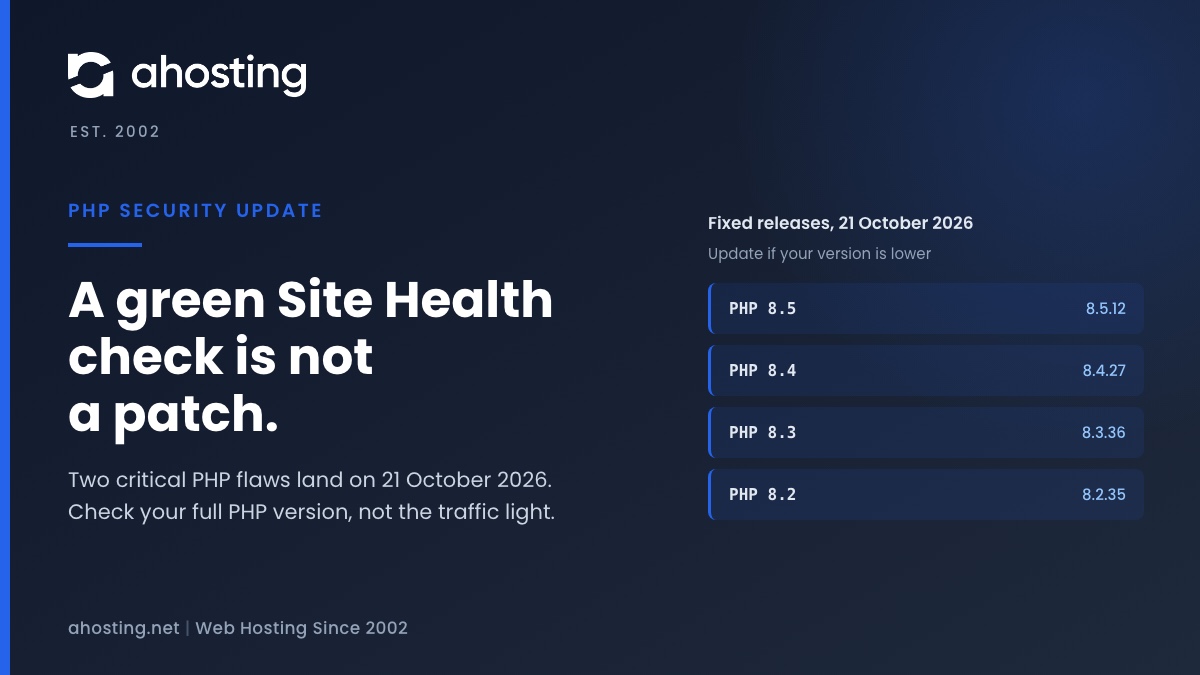
TL;DRPHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 are the php security update for two critical remote code execution flaws, released on 21 October 2026. Read your full PHP version now, and update if it is lower than the fixed release for your branch. A green WordPress Site Health check does not prove you are patched, and PHP 8.1 and older get no fix from PHP.
-
PHP Critical Security Release: What WordPress Site Owners Should Do Now
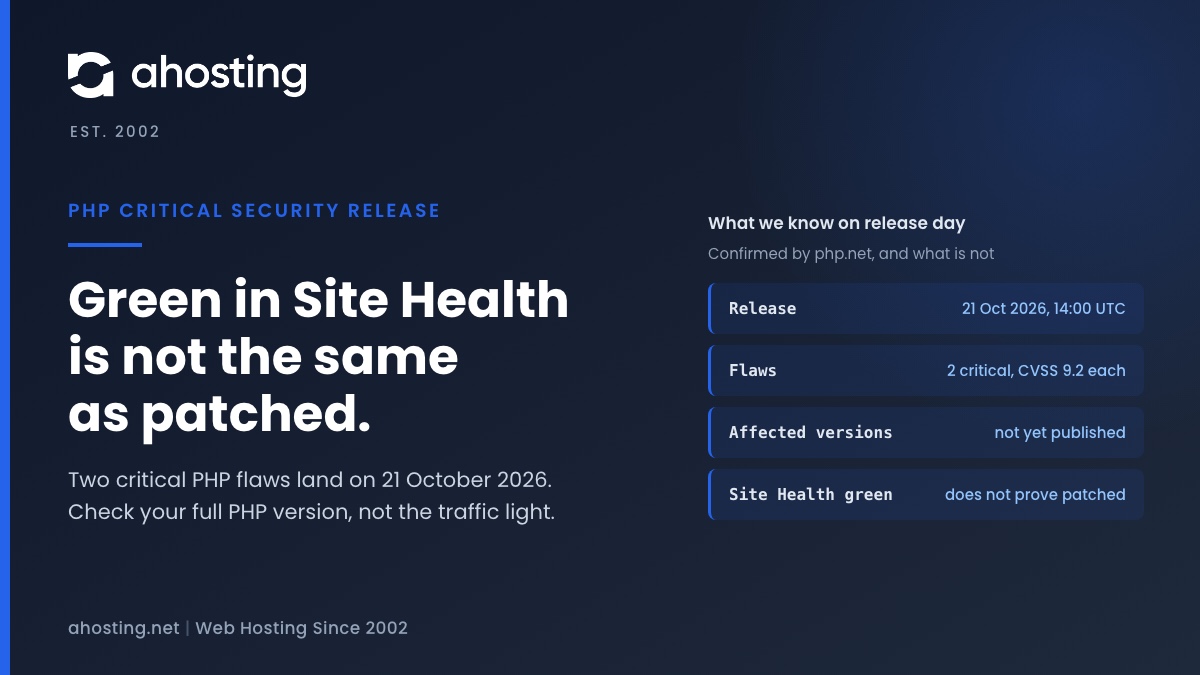
TL;DRThe PHP critical security release is due on 21 October 2026 at 14:00 UTC and fixes two flaws rated CVSS 9.2. PHP has not named the affected versions yet, so treat every WordPress site as exposed until it does. Check your full PHP version now, back up, and update as soon as the fixed version for your branch is published. A green Site Health PHP check does not prove you are patched.
-
Headers Already Sent in WordPress: Find the Byte | AHosting
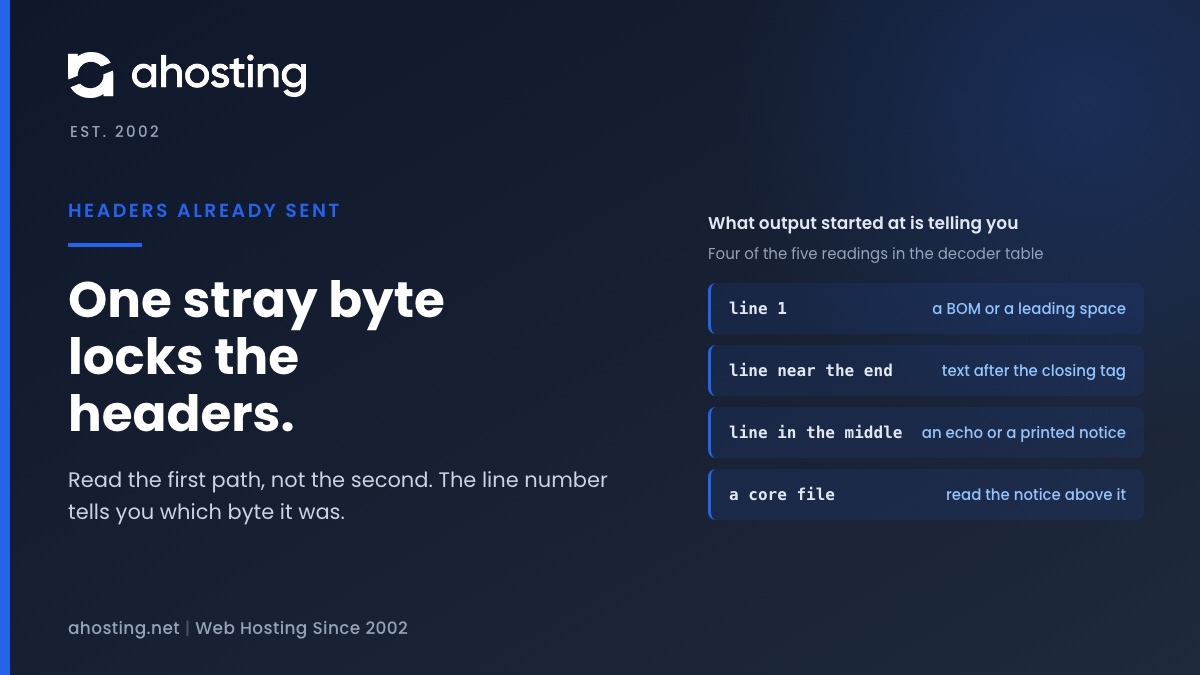
TL;DRThe headers already sent warning means PHP had already sent a byte of page output when WordPress tried to send a header or a cookie. Read the path after "output started at" first, because it names the file and line where that byte left. A line number of 1 points to a BOM, a line near the end points to text after a closing tag, and a core file points to a notice printed above it. In our lab a 3 byte BOM produced six warnings and no login.
-
Sorry, You Are Not Allowed to Access This Page in WordPress: Find the Cause
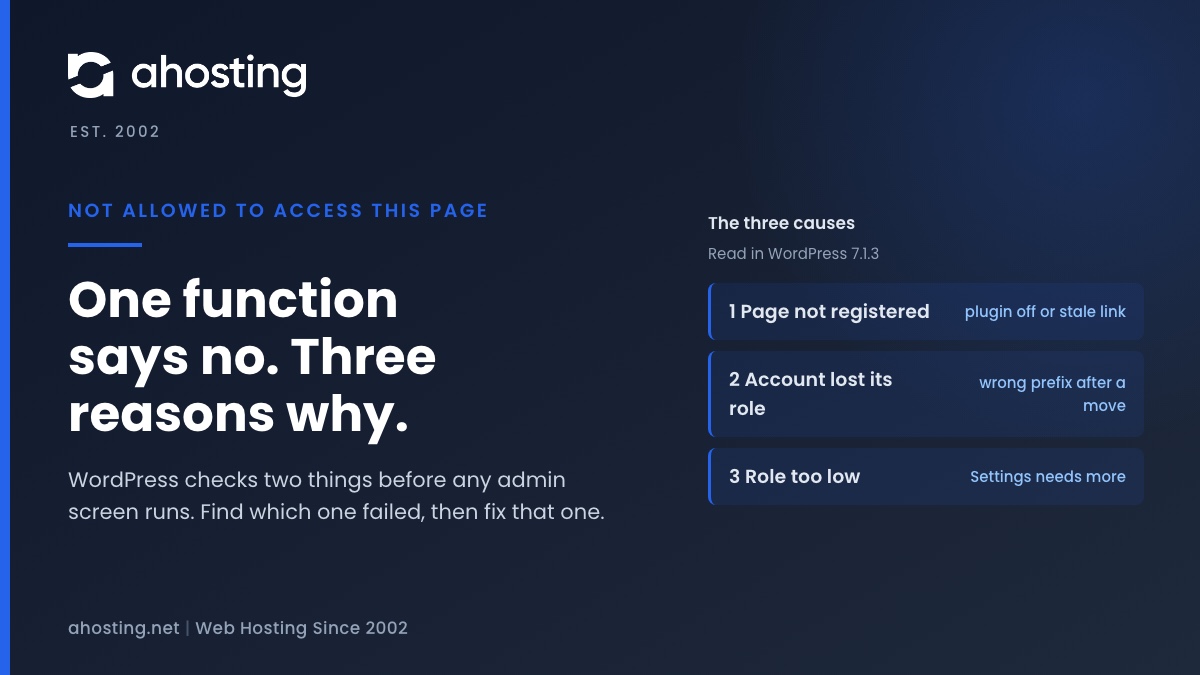
TL;DRWordPress prints "Sorry, you are not allowed to access this page." from one line in core, after one function answers no. That function refuses for three reasons: the page is not registered, your account has no role, or your role is too low. Open the Dashboard first. If it loads, check the plugin behind the address. If it fails too, the role records carry the wrong prefix.